Telekom Security Updates
Latest Update
Beyond the Binary: Hunting VS Code Tunnel Abuse
Executive Summary IDE tunneling (T1219.001) gives an intruder an interactive command-and-control channel from a stock, Microsoft-signed Visual Studio Code binary, over a Microsoft-owned relay, authenticated to an attacker’s GitHub account. Neither binary n...
Read the analysis
-
systemchk - DACH-Targeted VPN Credential Theft Toolkit
DescriptionThe analyzed archive contains a toolkit built to steal VPN credentials from enterprise endpoints. It covers twelve VPN products including Cisco AnyConnect, FortiClient, Palo Alto GlobalProtect, and Sophos. The attacker does no...
Continue Reading -
ABRTraryRoot: Local privilege escalation in Red Hat distributions
A chain of five bugs in ABRT allows any unprivileged local user to write attacker-controlled content into the root crontab, resulting in arbitrary command execution as root.We call the vulnerability chain “ABRTraryRoot” because it abuses...
Continue Reading -
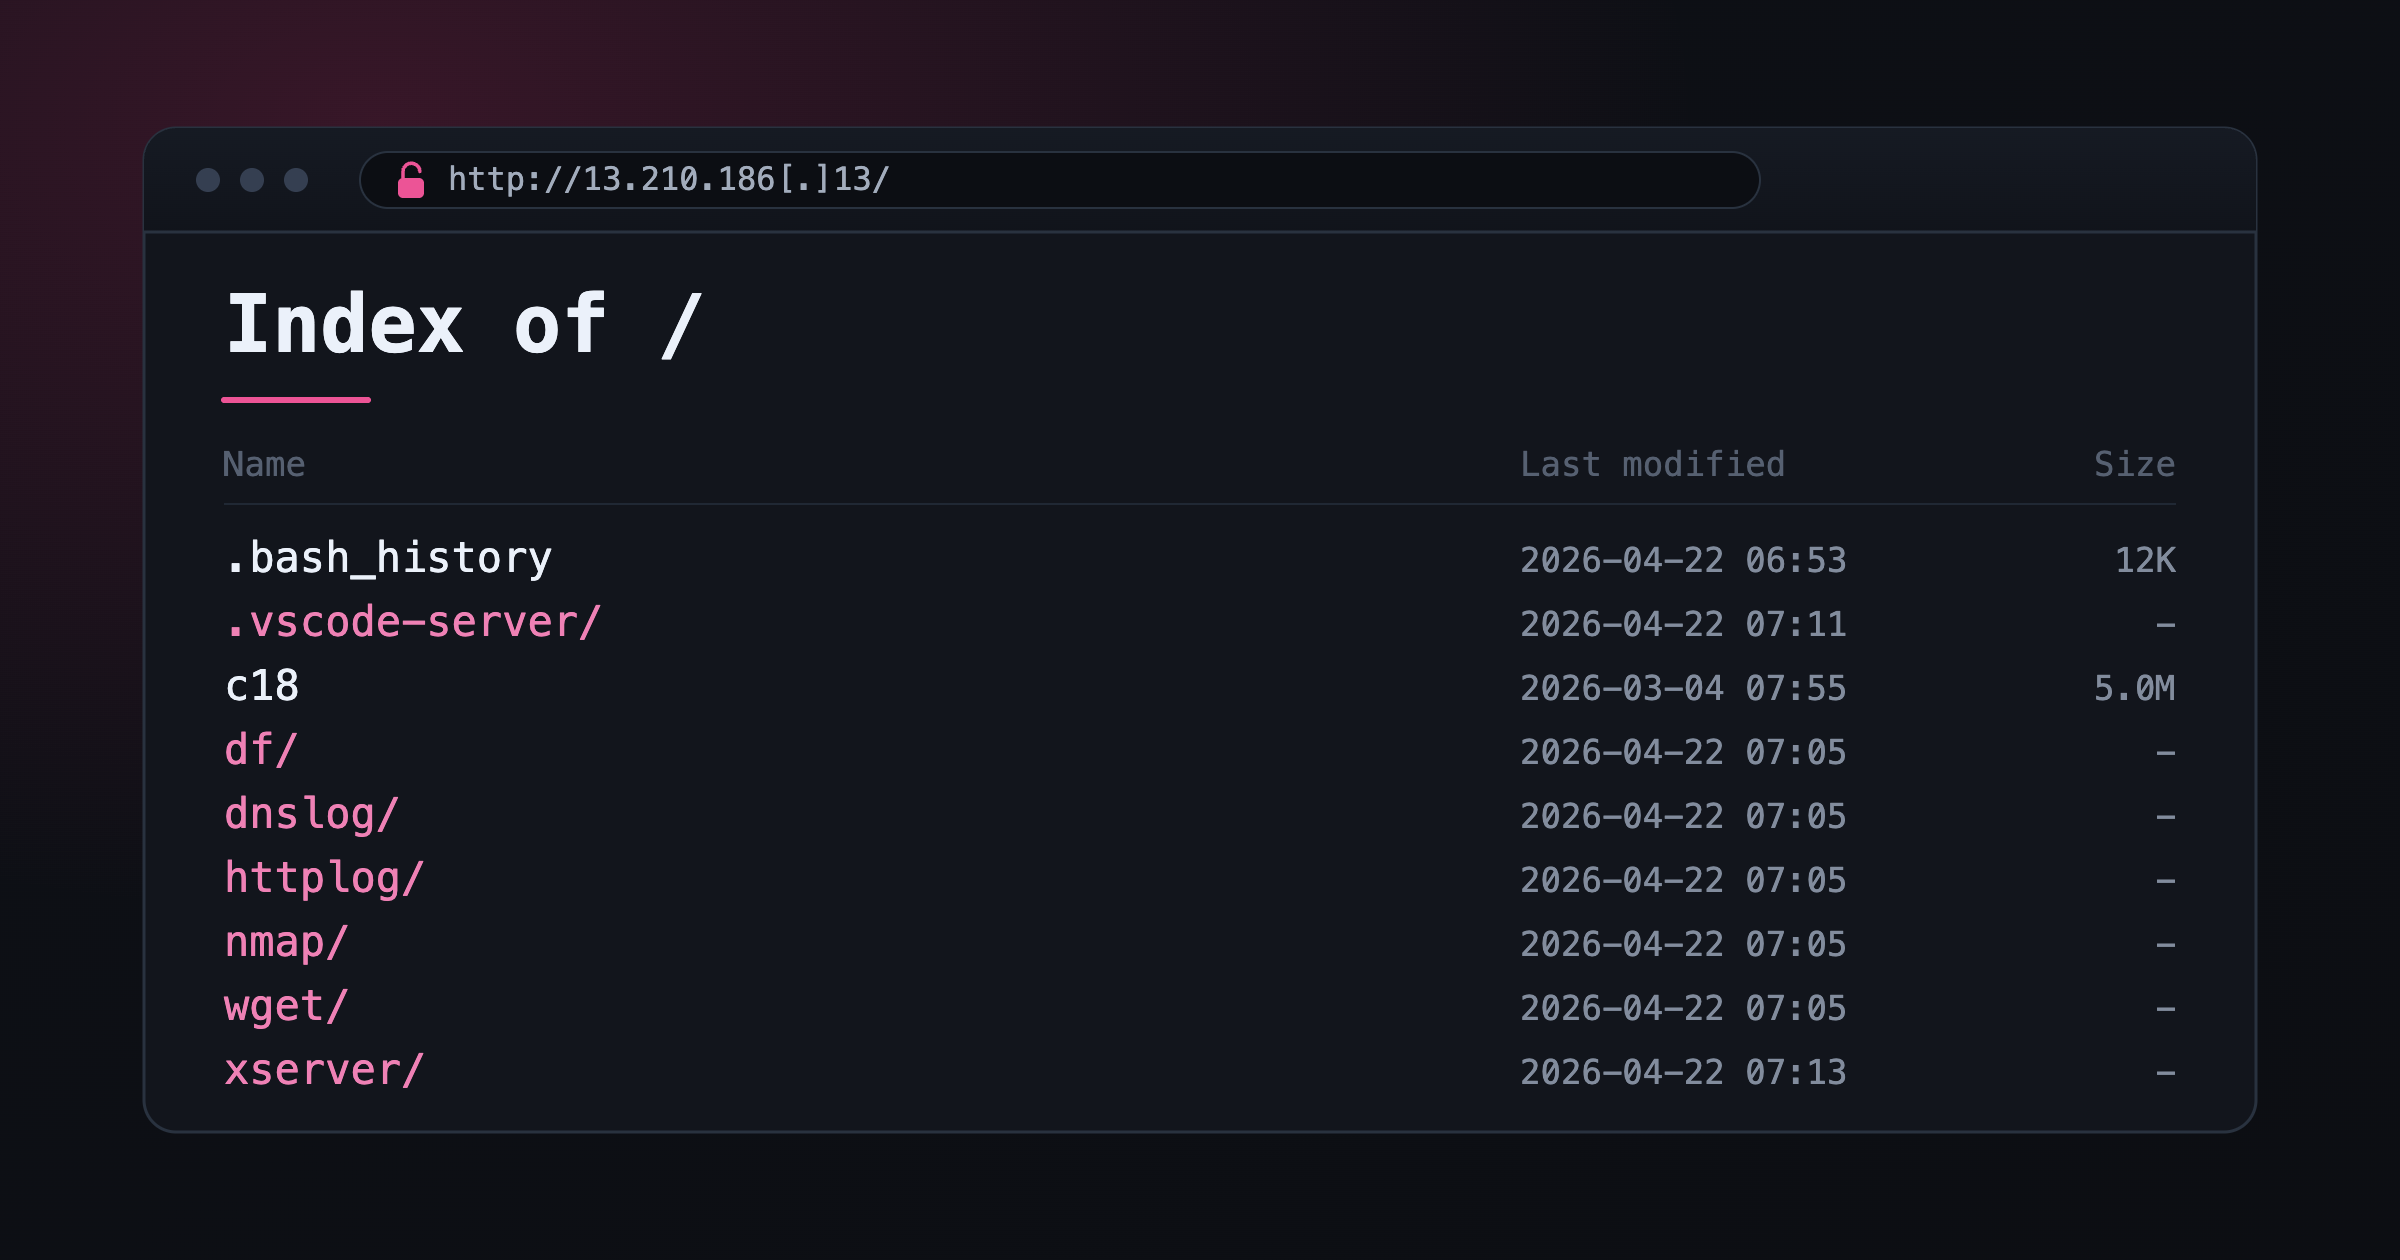
From Infected Zyxel to Exposed C2: A Case Study in IoT Botnet Operations
This report documents the identification of previously concealed operational infrastructure, including an exposed operator working directory and command-and-control (C2) environment, following the investigation of low-volume authenticati...
Continue Reading -
SetRootLanguage: Local privilege escalation in Ubuntu via AccountsService
A two-bug chain in Ubuntu’s AccountsService language update path allows any local user to obtain local root access. We call the vulnerability chain “SetRootLanguage” because a single call to the SetLanguage D-Bus method is all it takes t...
Continue Reading -
From Dropbox to Violet RAT v5: A Multi-Stage WebDAV Delivery Chain
Threat activity clusters rarely remain static over time. Delivery methods, lure formats, and payload choices often change between campaigns, while the underlying tradecraft remains stable enough to support tracking and detection. This re...
Continue Reading -
ZipLine-linked spearphishing campaign uses PowerShell backdoor and Cloudflare Tunnel
Telekom Security investigated a spearphishing campaign targeting organizations in several European countries. The campaign ultimately enables follow-on activity that, in at least one observed case, led to the deployment of Qilin ransomwa...
Continue Reading -
Pack2TheRoot (CVE-2026-41651): Cross-Distro Local Privilege Escalation Vulnerability
Today we publicly disclose a high-severity vulnerability (CVSS 3.1: 8.8) - in coordination with distro maintainers - that affects multiple Linux distributions in their default installations.The Pack2TheRoot vulnerability can be exploited...
Continue Reading